
Confidential business information can be among an organisation's most valuable assets. A company's competitive advantage may depend on proprietary processes, customer intelligence, pricing methods, source code, research, product plans or technical know-how. Unauthorised disclosure or use can undermine that advantage and cause commercial harm.
Trade-secret protection is not achieved simply by labelling information “confidential.” Businesses should identify information that genuinely warrants protection, limit access, document the circumstances in which it is shared, and apply reasonable contractual, organisational and technical safeguards.
What Qualifies as a Trade Secret?
Trade secrets generally involve information used in business that has value because it is not generally known or readily accessible to relevant competitors, and that its holder takes steps to keep confidential. Depending on the facts, examples may include:
-
Manufacturing methods, formulas and technical specifications.
-
Non-public source code, algorithms and software architecture.
-
Unpublished research, product roadmaps and development plans.
-
Non-public pricing, cost structures and negotiation strategies.
-
Confidential customer or supplier information, including commercially sensitive financial or purchasing data.
-
Proprietary operating procedures and technical know-how.
Not all business information is a trade secret. Publicly available information, information readily ascertainable through lawful means, and an employee's general knowledge, skills and experience will not automatically become the employer's exclusive property merely because the employer calls them confidential.
The Legal Framework in India
India does not currently have a single, comprehensive standalone trade-secrets statute. Depending on the facts, protection may arise through contractual obligations, breach-of-confidence principles, and other applicable laws. The legal basis and available remedy should be assessed for each case.
-
Contract: NDAs, employment agreements and commercial contracts can define permitted use, restrict disclosure and establish return or deletion obligations. Their enforceability depends on the wording, facts and applicable law.
-
Breach of confidence: Courts may restrain misuse of confidential information where the legal requirements are met. In John Richard Brady & Ors. v. Chemical Process Equipments Pvt. Ltd., the Delhi High Court granted interim injunctive relief concerning technical drawings, specifications and know-how allegedly disclosed in confidence and used beyond the permitted purpose.
-
Other laws: The Copyright Act, 1957 may protect qualifying original works such as software code and drawings, but copyright does not create a general monopoly over facts or ideas. The Information Technology Act, 2000 and applicable data-protection or sector-specific laws may also be relevant in particular circumstances. These laws should not be treated as automatic protection for every confidential item.
Identify and Classify Sensitive Information
An information audit should identify what information the business holds, where it is stored, who can access it, why it has commercial value, and what could happen if it were disclosed. A practical scheme can distinguish public information, ordinary internal information and restricted confidential information. The most sensitive items should have named owners, access rules, storage requirements and periodic reviews.
Use Clear Non-Disclosure Agreements
An NDA is useful when sharing information with employees, consultants, suppliers, manufacturers, prospective investors or commercial partners. It should be tailored to the relationship and address:
-
The categories of confidential information, avoiding definitions that are needlessly vague.
-
The purpose for which the recipient may use the information.
-
Limits on access, copying, onward disclosure and use by subcontractors.
-
Appropriate exclusions, such as information already lawfully known or becoming public without breach.
-
The duration of obligations, including continuing protection for information that remains a trade secret.
-
Return, deletion or destruction of information, subject to lawful retention and backup requirements.
-
The process for legally compelled disclosure and prompt notice where legally permitted.
An NDA does not replace security controls, and signing one does not by itself prove that all information covered by it qualifies as a trade secret.
Employment Agreements and Employee Mobility
Employment agreements should impose clear duties to use company confidential information only for authorised work, safeguard it, disclose suspected incidents and return company materials when employment ends. Policies should explain how employees handle source code, customer data, internal financial information, research and product plans.
In American Express Bank Ltd. v. Priya Puri, the Delhi High Court considered claims involving customer information, alleged trade secrets and a departing employee. The decision is a caution against treating every customer name or professional relationship as automatically proprietary: the character of the information and the evidence matter. Businesses should distinguish genuinely sensitive non-public data from information that is publicly accessible and from an employee's general skills, experience and relationships.
Confidentiality clauses should not be used as a disguised blanket prohibition on future employment. Section 27 of the Indian Contract Act, 1872 generally addresses agreements in restraint of trade; post-employment restrictions require careful, jurisdiction-specific legal review.
Technical and Organisational Safeguards
-
Least-privilege access: Give employees access only to information needed for their roles.
-
Authentication: Use multi-factor authentication for important accounts and systems.
-
Encryption: Protect sensitive information in transit and, where appropriate, at rest.
-
Logging and monitoring: Keep proportionate records of access and administrative activity.
-
Secure devices and backups: Apply updates, device controls and protected backup practices.
-
Data-loss prevention: Where proportionate, monitor or restrict unauthorised transfers.
-
Training: Teach staff how to handle confidential information and recognise phishing and social engineering.
Controls should be proportionate to the organisation's size, industry, risk profile and the sensitivity of the information. A policy that is never implemented may be less persuasive than a practical system consistently used.
Sharing Information With Third Parties
Before disclosing confidential information, confirm that the recipient needs it and that disclosure is necessary for a defined purpose. Use due diligence, an appropriate NDA, restricted access, records of what was shared, limits on onward disclosure and a process for revoking access when the relationship ends.
John Richard Brady is particularly relevant to technical drawings and know-how disclosed in a commercial context. The judgment supports the importance of limiting the purpose of disclosure and preventing use outside the circumstances in which confidential material was supplied.
Offboarding and Employee Departures
-
Revoke access to systems and shared workspaces at the appropriate time.
-
Recover company-owned devices and storage media.
-
Transfer ownership of business accounts, repositories and project records.
-
Remind the departing employee of continuing confidentiality obligations.
-
Request return or deletion of company information where appropriate and lawful.
-
Preserve relevant evidence if a suspected breach is identified.
The objective is to protect identifiable confidential information not to claim ownership over everything a person remembers or prevent lawful employment mobility.
Responding to Suspected Misappropriation
-
Preserve evidence: Secure relevant access logs, communications, contracts and system records.
-
Assess secrecy: Determine what information is at issue, whether it was public, and what safeguards existed.
-
Contain the incident: Secure accounts and systems and prevent further unauthorised access where possible.
-
Get legal advice: Assess contractual remedies, possible injunctions, damages and evidentiary requirements.
-
Review controls: Address weaknesses in access, training, contracts and information handling.
Businesses should avoid unsupported accusations or attempts to obtain a competitor's confidential information through unlawful means.
Limits of Trade Secret Protection
Trade-secret protection does not ordinarily grant a monopoly over an idea or invention against the world. Depending on the facts and applicable law, independent development, lawful acquisition, public availability or legitimate reverse engineering may affect whether a claim can succeed. The result also depends on how the information was obtained and used, and on the relevant contractual obligations.
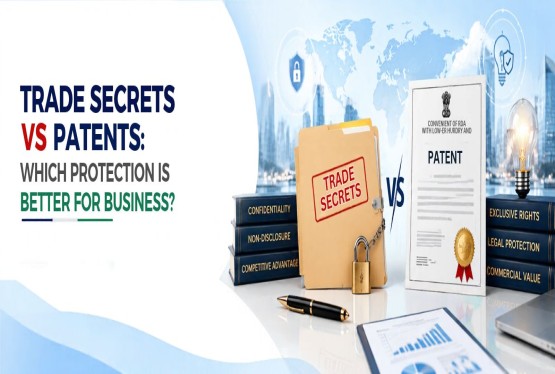
Businesses should therefore choose a protection strategy that fits the asset. Some information is best kept secret; some innovations may be candidates for patent protection; and qualifying original expression may be protected by copyright. These regimes are different and should not be conflated.
Conclusion
Protecting confidential business information through trade secrets requires a combination of clear contracts, limited access, practical security controls, employee training and careful information-sharing procedures. Indian decisions such as John Richard Brady v. Chemical Process Equipments and American Express Bank v. Priya Puri illustrate both the potential for protecting genuinely confidential information and the need to distinguish it from public information and general professional knowledge.